Frameworks
Mapped frameworks and the AI regulatory clock.
Which frameworks ColossalX maps to or assesses against, in the exact words, and the dated deadlines that change what your teams must show.
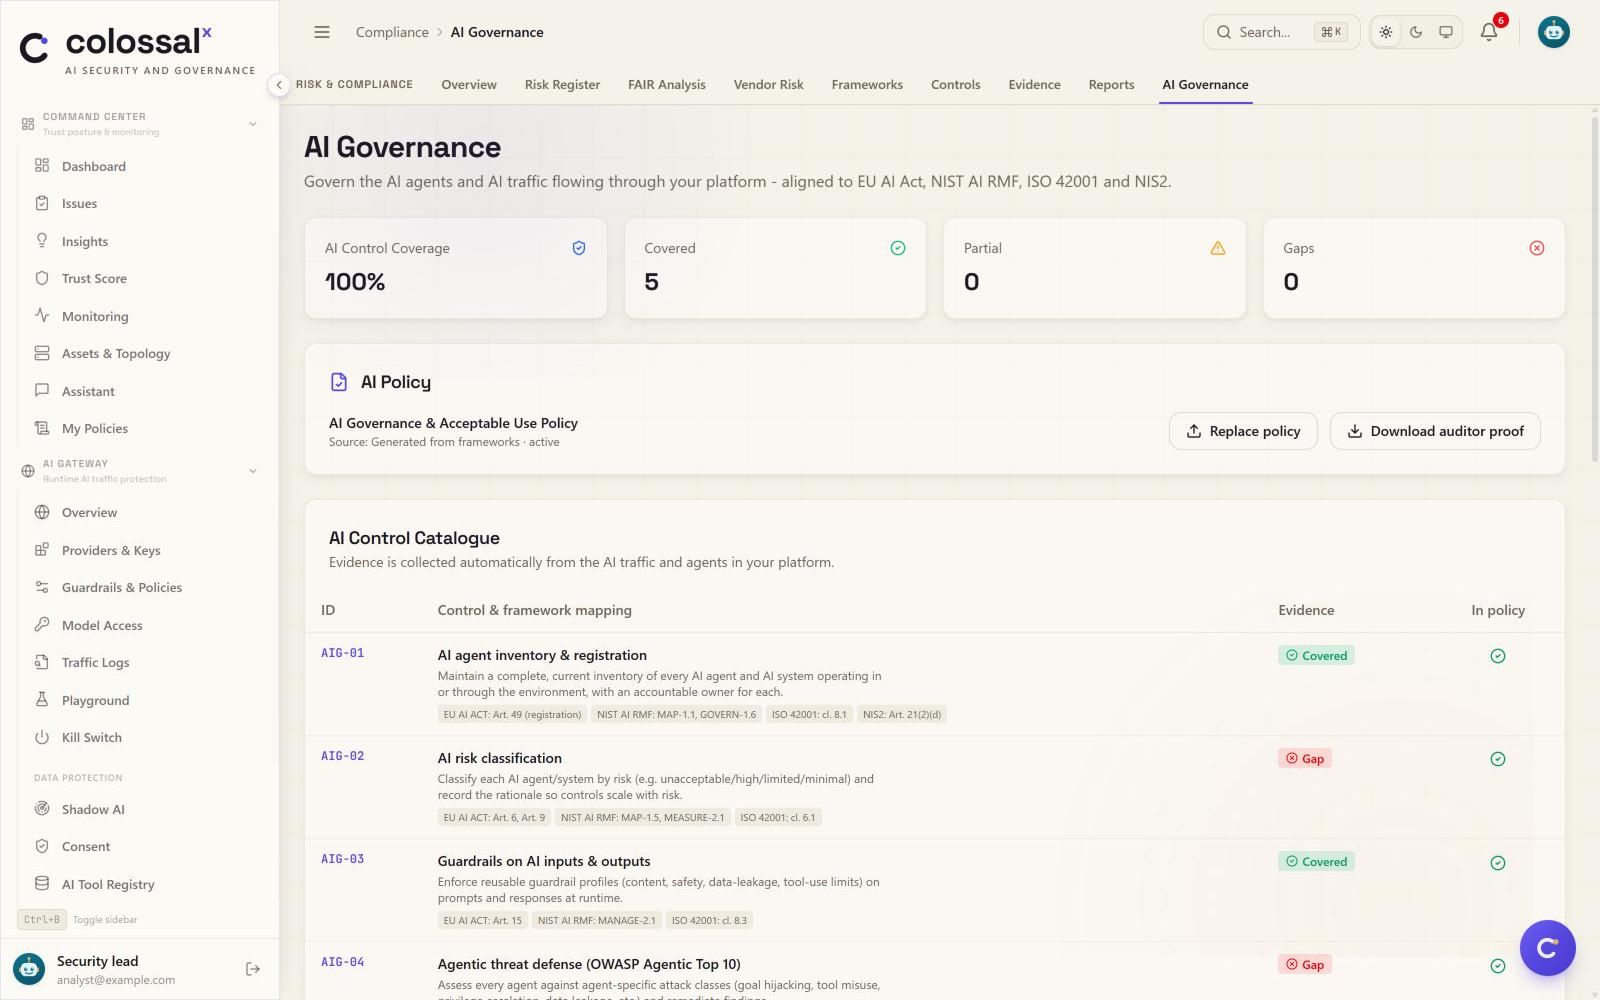
One control, many clauses: AI agent inventory and registration maps to EU AI Act (Art. 49); NIST AI RMF (MAP-1.1, GOVERN-1.6); ISO/IEC 42001 (cl. 8.1). Mapped to and assessed against, not certified.
In short
ColossalX relates to each framework in one stated way. Governance and privacy frameworks are mapped to controls assessed from live signals; the OWASP and MITRE lists are assessed against or covered in testing; RBI FREE-AI and the CERT-In blueprint are context only. The regulatory clock shows dated deadlines, each with its source.
Vendor framework badges promise outcomes no tool can deliver, and an auditor cannot check them.
ColossalX states its relation to each framework and keeps the evidence behind each mapped control.
Mapped to
Mapped to: governance, privacy and sector rules.
Controls are mapped to clauses and assessed from live signals, with one score per framework, trended nightly, and the evidence behind each control. Open a framework for what it is.
NIST AI RMFMapped to
The voluntary US framework to govern, map, measure and manage AI risk.
EU AI ActMapped to
The EU law on AI systems, with duties phased in by risk level.
ISO/IEC 42001Mapped to
The international standard for an AI management system.
SOC 2Mapped to
The AICPA framework for reporting on a service organisation’s controls.
GDPRMapped to
The EU regulation on personal data, including data that reaches AI.
India DPDPMapped to
India’s Digital Personal Data Protection Act, 2023, and its rules.
SEBI cyber circularsMapped to
Cyber security and resilience circulars for India’s securities markets.
IRDAI cyber circularsMapped to
Information and cyber security guidelines for India’s insurers.
PCI DSSMapped to
The payment card industry’s data security standard.
NIS2Cross-mapped to
The EU directive on network and information security; AI controls cross-map to it.
3notes
- One control, many clauses
- Evidence status per control
- A gap is shown
Assessed against
Assessed against: the attack and threat lists.
Security lists are tested, not just mapped: each agent is assessed, and coverage comes from authorised runs through your real controls.
In detail4
- OWASP Agentic Top 10. ASI01 to ASI10. Assessed per agent against this list.
- OWASP LLM and MCP Top 10. Covered in probes and scans, alongside the agentic list.
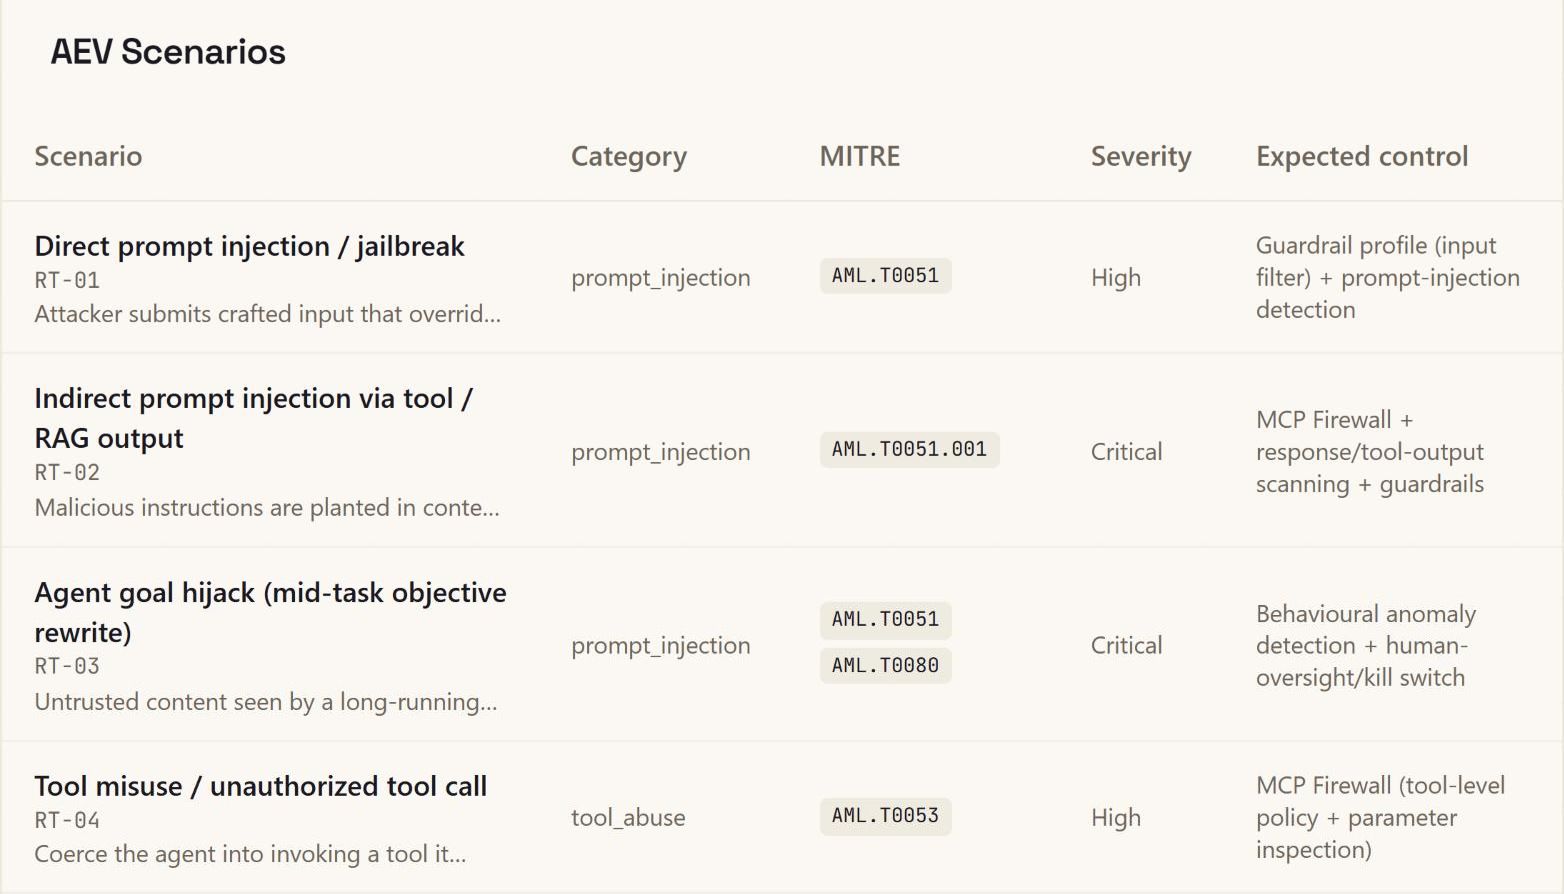
- MITRE ATLAS. Coverage measured from runs: exercised, exercisable and untestable.
- MITRE ATT&CK. Detections mapped to it: behavioural detections carry its techniques.
2notes
- ATLAS technique per scenario
- Expected control named
Regulatory clock
The AI regulatory clock, dated and sourced.
The dates that change what AI governance teams must show, and what each asks. Each comes from a named source, and dates can move.
In detail4
- 2 Aug 2026 EU AI Act. Article 50: tell people they are dealing with AI, and mark AI-generated content.
- 13 Nov 2026 India DPDP. Consent managers can register and act for people managing their consent.
- 13 May 2027 India DPDP. Notice, consent, safeguards, breach reporting and individual rights take effect.
- 2 Dec 2027 EU AI Act. Annex III high-risk systems, such as credit scoring and hiring, must meet the Act.
Sources: Jones Walker, AI law blog; PIB, DPDP Rules 2025; PIB, DPDP Rules 2025; Gibson Dunn. Checked 6 Oct 2026.
Regulatory clock · dated: 2 Aug 2026 AI Act Article 50; 13 Nov 2026 DPDP consent managers; 13 May 2027 DPDP core obligations; 2 Dec 2027 AI Act Annex III.
Relation words
What each relation word means.
The words are fixed, so no page can drift into a claim no tool could stand behind.
RBI FREE-AIContext only
Read for context in India; ColossalX does not tie its controls to it.
CERT-In AI blueprintContext only
Read for context in India; no control is tied to it either.
Not assessableAn honest answer
When the evidence cannot decide a control, it says so, rather than passing or failing it.
Health beside statusTwo views
Each control shows a measured health label beside the status a person decided.
Relation words · what they mean: Mapped to ends in controls linked to clauses; Cross-mapped to ends in via another framework; Assessed per agent against ends in configured controls, per agent; Covered in probes and scans ends in attacks and checks tagged; Coverage measured from runs ends in exercised versus exercisable; Context only ends in read, never tied.
Honest by design
What a mapping does not mean.
Frameworks · stated plainly: Relation words fixed, from one list; Certificates none claimed; RBI, CERT-In context only; Dates sourced, re-checked at review. Mapped, not certified.
x, not measured
Mapping a control to a clause is not the same as meeting the law or standard.
All 4 limits
- ColossalX holds no certifications; SOC 2 and ISO/IEC 42001 here describe mappings only.
- India and EU packs are starting content for your counsel to review, not legal advice.
- Dates come from the sources named and can move; each is re-checked at review.
Questions
Questions buyers ask
When do EU AI Act high-risk obligations apply?
According to the source on our clock, Annex III high-risk obligations apply from 2 Dec 2027, and the Article 50 transparency obligations applied from 2 Aug 2026. EU decisions can move these dates, so the clock names its source for each one and we re-check them at every review. Treat it as orientation, and confirm with counsel.
When do India’s DPDP obligations apply?
Under the Digital Personal Data Protection Rules published by the government, the consent manager rules start on 13 Nov 2026 and the core obligations on 13 May 2027. ColossalX is mapped to India DPDP and enforces consent for AI requests at runtime; it is not a consent manager in the regulatory sense.
What does “mapped to” mean on this page?
It means ColossalX links its controls to specific clauses of that framework, assesses those controls from live signals and keeps the evidence behind each one. It does not mean a certificate, and it does not mean your organisation meets the framework: that depends on your systems, your processes and, where relevant, an auditor.
How do NIST AI RMF and ISO/IEC 42001 fit together?
NIST AI RMF is a voluntary US framework organised around four functions: govern, map, measure and manage AI risk. ISO/IEC 42001 sets requirements for an AI management system that an organisation can be audited against. Many teams use the first to decide how to manage AI risk and the second to run that work as a system. ColossalX maps AI-governance controls to both.
Can a tool deliver EU AI Act conformity on its own?
No. Conformity depends on your AI systems, how you use them and, for some systems, a formal assessment. ColossalX maps its controls to the Act’s articles, assesses them from live signals and keeps graded, timestamped evidence: that is part of the work an assessor will look at, not all of it.
Why are RBI FREE-AI and the CERT-In blueprint context only?
Because ColossalX does not tie its controls to them today. They shape how Indian regulated firms think about AI, so they appear here for context, and the India pack carries starting content for your counsel to review. We would rather say context only than imply a relation we cannot show evidence for.
Next step
Know your framework x.
See your frameworks mapped, your agents assessed and your evidence collected, on your own estate.
- 01Tell us your frameworks
- 02See the controls mapped
- 03Decide what to show first