Security at ColossalX
How ColossalX protects itself, and your data.
Each customer in its own workspace and database, keys sealed at rest, sign-in you control, and our own SBOM and AI-BOM on request.
Security at ColossalX · in brief: Isolation Own workspace and database; Sign-in SAML SSO, MFA by role; Keys Provider keys sealed at rest; Assurance SBOM and AI-BOM on request. Stated, not implied.
In short
Security at ColossalX starts with isolation: each customer runs in its own workspace with its own database, subdomain and TLS. Provider keys are sealed at rest, sign-in uses SAML SSO with MFA required by role, access is scoped to custom roles, evidence is timestamped daily, and procurement can request ColossalX's own SBOM and AI-BOM.
An AI security vendor holds your prompts, keys and findings, so it joins your attack surface.
Each customer is isolated in its own database, keys are sealed, and access is scoped by role.
Isolation
Your own workspace, your own database.
Each customer runs in an isolated workspace, created in one step with its own database, its own subdomain and TLS.
Own database
Your records live in a database that no other customer shares.
Own address
Your workspace is served over TLS on a subdomain of its own.
Modules you switch on
Only the modules switched on for your workspace are active in it.
Hosting
Hosted in India, with a backup in the United States. Each customer workspace can run in another region on request. Databases are encrypted at rest.
One customer · one workspace: your agents to your workspace; your people to your workspace (SSO, MFA); your workspace to your database (isolated); your workspace to provider keys.
Access
Sign-in you control, access scoped by role.
People sign in through your identity provider, agents carry their own credentials, and each role sees only what it is given.
Single sign-on
SAML SSO with just-in-time provisioning, Microsoft and Google sign-in, and Entra directory sync.
Roles to the page
Directory groups map to roles; custom roles reach down to the page; MFA is required by role.
Agents prove who they are
Per-agent credentials, with post-quantum hybrid identities; the private key can stay with the agent.
Keys and connections
Provider keys are sealed at rest; connections can be disconnected or revoked; API keys always expire.
An assistant inside your role
Its actions ask you to confirm first and run under your own role.
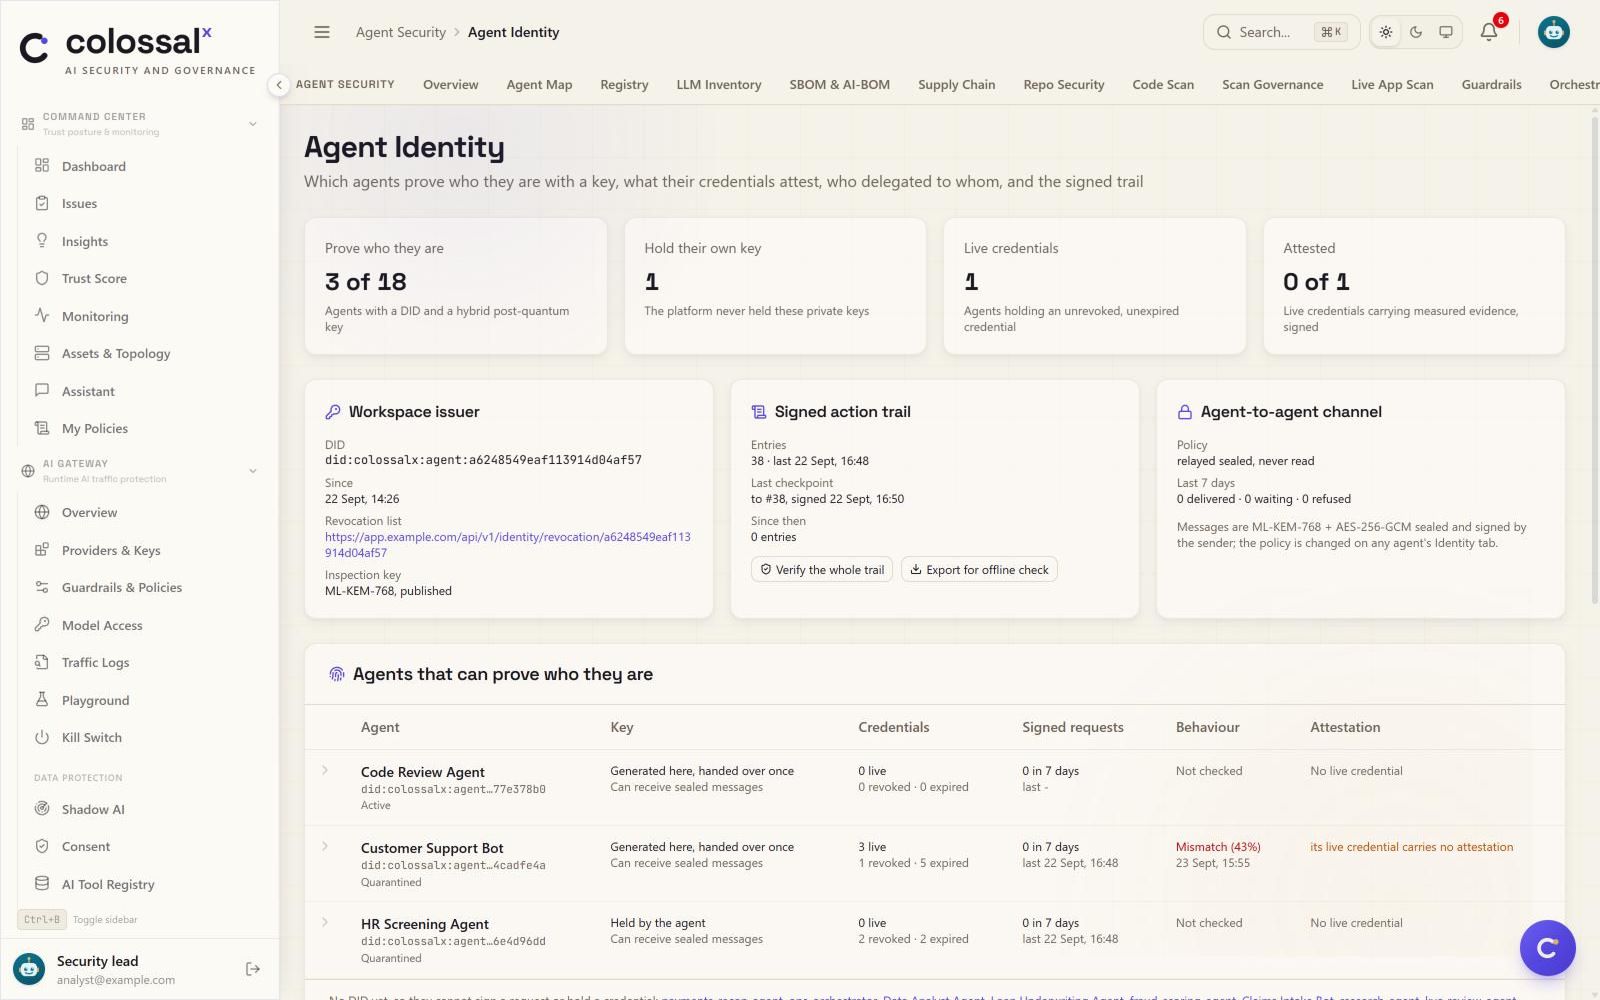
3notes
- Agent holds its key
- Public revocation list
- Verify the whole trail
Evidence
Records you can re-check, not just read.
What ColossalX records is kept so that someone other than us can check it later.
Sealed run manifests
Each test run is sealed, and the seal is re-checked when the run is read.
Daily timestamps
Evidence keeps byte-exact originals and a daily trusted-timestamp manifest.
Withdrawn, never deleted
Withdrawn evidence is kept, and retention flags, archives or anonymises; it never hard-deletes.
Who and why
Approvals, sign-offs and containment keep who decided and why.
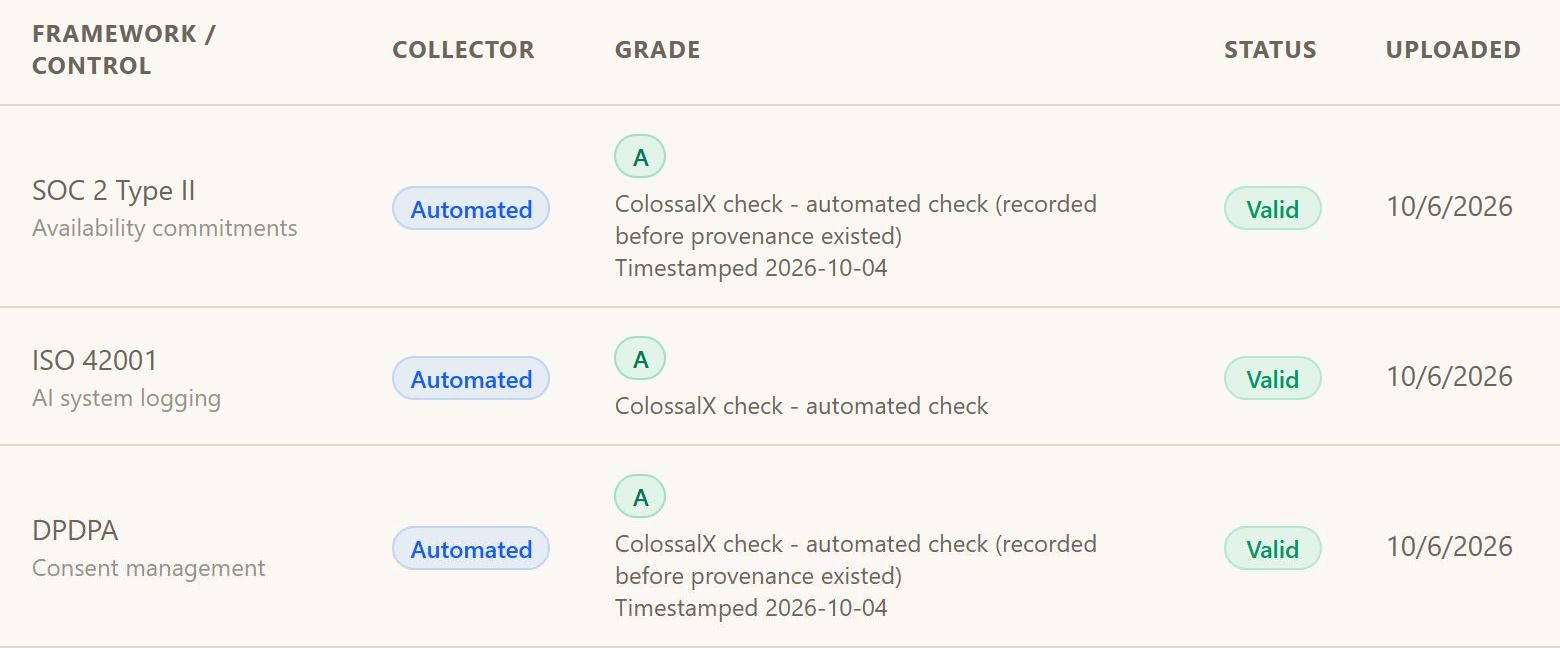
3notes
- Mapped to a control
- Graded by how obtained
- Timestamped, still valid
Our own AI
We govern our own AI the way we govern yours.
ColossalX uses AI in some of its own features. You choose where that AI runs, and procurement can see what the platform is made of.
Where its AI runs
Managed, your own key or self-hosted; its internal AI calls are recorded.
Fallback warnings
A warning shows when a role runs on a fallback model.
SBOM and AI-BOM
Our own SBOM and AI-BOM in CycloneDX 1.6, on request, with no model bundled or run locally.
Read, never run
Code a model hands an agent is inspected, never run; model files are scanned, never executed.
Report a vulnerability
Write to client.success@quantexra.tech, the address in our security.txt file.
Our own AI · your choice: insights brief to ColossalX (internal AI call); ColossalX to managed model; ColossalX to your own key (your choice); ColossalX to self-hosted.
Honest by design
What we will not tell you.
Before it leaves · redaction: support-agent to provider A · outside model, "Update the card ending 4242 for this customer". Checks: Personal data flagged, Prompt injection passed. Verdict: redacted, Card number redacted first.
x, not measured
ColossalX holds no certification; frameworks are mapped to and assessed against.
All 3 limits
- ColossalX is delivered as SaaS only; each customer runs in its own workspace and database.
- What reaches an outside model provider is then held on that provider's terms; redaction runs first.
Questions
Questions buyers ask
How is each customer's data isolated?
Each customer runs in an isolated ColossalX workspace with its own database, served over TLS on its own subdomain and provisioned in one step. Modules are switched on per workspace, people sign in through your identity provider, and roles scope what each person can see and do, down to the page.
Can we get ColossalX's SBOM and AI-BOM for our review?
Yes, on request. The vendor assurance pack holds ColossalX's own SBOM and AI-BOM in CycloneDX 1.6, with a checked statement that no model is bundled with the platform or run locally. Ask for it through client.success@quantexra.tech or during your walkthrough.
How does ColossalX govern its own AI features?
The way it governs yours. You choose where its AI features run: on a managed model, with your own key or self-hosted. Its internal AI calls are recorded, a warning shows when a role runs on a fallback model, and the insights it writes must cite the measurements behind them.
How do we report a vulnerability?
Email client.success@quantexra.tech with what you found and how to reproduce it. The same address is published in the site's security.txt file, at /.well-known/security.txt, for researchers and automated tools. A person at Quantexra Labs reads each report and replies by email.
Does ColossalX hold security certifications?
No. ColossalX holds no certification, and it does not imply one. The frameworks it maps your controls to, such as SOC 2, ISO/IEC 42001 and NIST AI RMF, are mapped to and assessed against, never certified. For a vendor review, it provides its own SBOM and AI-BOM on request.
Next step
Know your x, including ours.
See ColossalX's own controls in a walkthrough: isolation, sign-in, evidence and the parts list.
- 01Tell us what you run
- 02See the four verbs on it
- 03Decide where to start