SolutionsFor risk and compliance

For risk and compliance: know where you stand.

A risk register that fills itself, AI risk in money, controls assessed from live signals and audits that end in a sealed archive.

Audit archive · sealedIllustrative

Audit archive · sealed: Plan Risk-based, approved; Tests Design, then operation; Samples Replay identically; Findings With management response. Sealed and timestamped.

In short

AI risk and compliance management, in ColossalX, is a register that fills itself from compliance gaps, audits, scans, proven attacks and intelligence, AI risk quantified in money with FAIR, frameworks assessed from live signals with one score per framework, and an audit lifecycle that runs from a risk-based plan to a sealed, timestamped archive.

Last reviewed

The question you are asked

Where do we stand against our frameworks, in money and in evidence?

For risk and compliance

What auditors ask, and what answers it.

  1. The risk register is a spreadsheet, current for one committee meeting.

    The controlThe register fills itself from gaps, audits, scans, proven attacks and intel, quantified with FAIR.

  2. A control shows green because nobody could test it.

    The controlA control nobody could assess is marked not assessable and excluded, never quietly passed.

  3. The same person prepared and reviewed the audit work.

    The controlThe preparer never reviews and the signer never prepares; the archive is sealed.

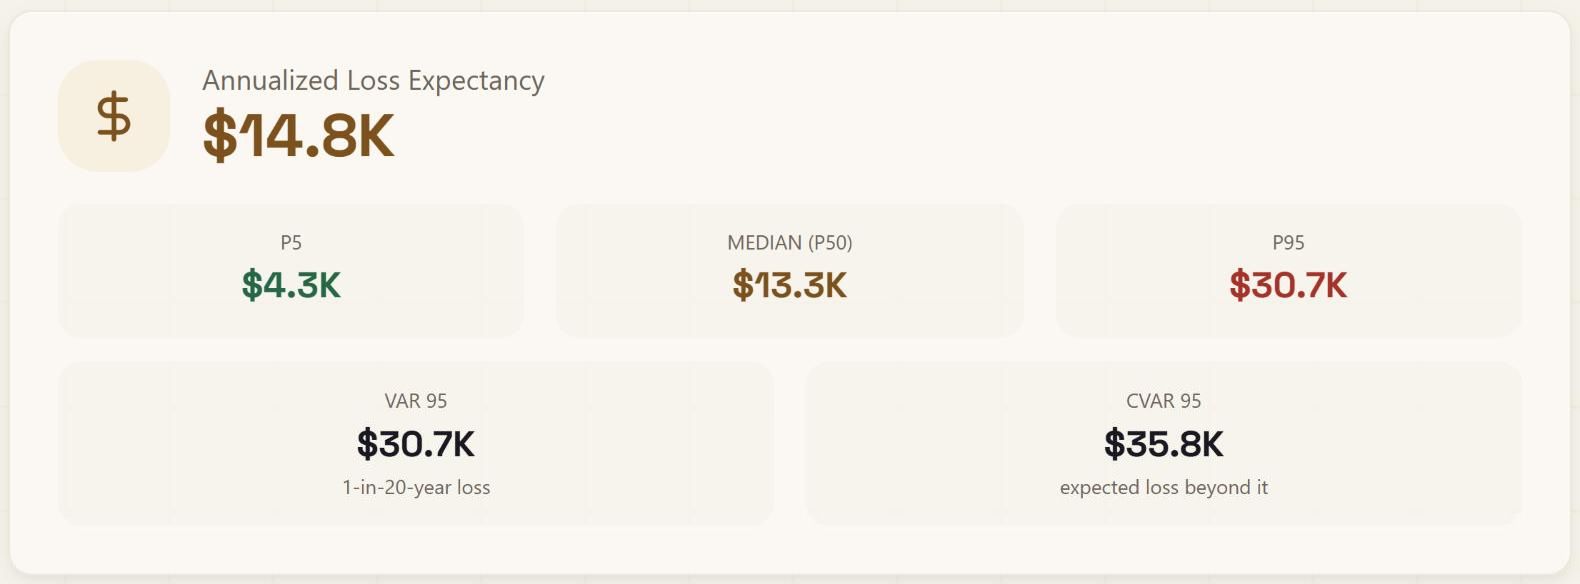
A FAIR analysis in a demo workspace: one AI-governance gap expressed as an expected annual loss in money, with the range it is likely to fall in and the expected loss in the tail beyond a one-in-twenty-year event.
From a demo workspace
3notes
  1. Expected loss per year
  2. The likely range
  3. The tail beyond it

The board

Questions the audit committee will ask.

Where do we stand against our frameworks?

One score per framework, trended nightly, with not assessable shown as an answer.

What is our AI risk in money?

A FAIR loss range with its tail, held against the board appetite.

Will the audit trail hold up?

Preparer never reviewer, signer never preparer, and a sealed, timestamped archive.

One control · three frameworksIllustrative

One control · three frameworks: Guardrails on AI inputs and outputs maps to EU AI Act (Art. 15); NIST AI RMF (MANAGE-2.1); ISO/IEC 42001 (Clause 8.3). Mapped to and assessed against, not certified.

ColossalX

One-page brief · For risk and compliance

Risk and compliance, mapped and evidenced

ColossalX, from Quantexra Labs, is an AI security and governance platform delivered as SaaS. It keeps a quantified AI risk register, assesses controls from live signals and runs audits.

Read the full brief

What it does

  • A self-filling register, quantified with FAIR.
  • Controls assessed from live signals, scored per framework.
  • Audits from risk-based plan to sealed archive.

Ask any vendor

  1. What does an untested control show?
  2. Can a finding close without positive evidence?
  3. Who prepared this work, and who reviewed it?

LimitJurisdiction packs are starting content for counsel; no certification is held.

https://colossalx.tech/solutions/risk-complianceclient.success@quantexra.techSaaS, each customer in its own workspace and databaseWritten for a risk or compliance lead · last reviewed 6 Oct 2026

Honest by design

What we will not tell you.

Control validation · one controlIllustrative

Control validation · one control: Status Not assessable; Reason No source could be read; Score Excluded, not failed; Decided by A named person. Reason recorded.

x, not measured

Jurisdiction-pack content and regulator page-watch candidates are starting points for your counsel to review.

All 3 limits
  • Cloud posture is assessed for AWS only.
  • ColossalX holds no certification; frameworks are mapped to and assessed against.

Questions

Questions buyers ask

How do you manage AI model risk?

Start with an inventory of the models, agents and third-party AI in use, assess each one, then test, monitor and record who decided what. ColossalX keeps that inventory, flags AI vendors that are in use but not assessed, quantifies risk in money with FAIR and holds it against your risk appetite, escalating acceptances beyond appetite to the board.

How are AI controls tested and evidenced?

Controls are assessed from live signals, and recent tests count as control evidence. Each control carries a health label beside the status a person decided, with a reason per control. Evidence collects itself, graded A to D by how it was obtained, verified by a second person, timestamped daily and withdrawn, never deleted.

How does ColossalX track regulatory change?

Jurisdiction packs for global, India, EU and US rules carry regulatory reporting clocks, and a regulator page-watch raises candidates that a person confirms. The content is a starting point for your counsel to review, not legal advice, and a compliance calendar is built from your own records.

Can risks and findings sync to our GRC tool?

Yes. Risks sync out to GRC, ticketing and third-party risk tools, and findings become issues with an owner, a due date and a ticket in the tool that will close it. An issue closes only on positive evidence, not on a ticket status, and a risk acceptance must expire.

Next step

Can you account for x?

See ColossalX on your frameworks, your register and your next audit, with the person who will own it.

  1. 01Tell us what you run
  2. 02See the four verbs on it
  3. 03Decide where to start